Azure Attestation explained: cryptographic proof for confidential computing
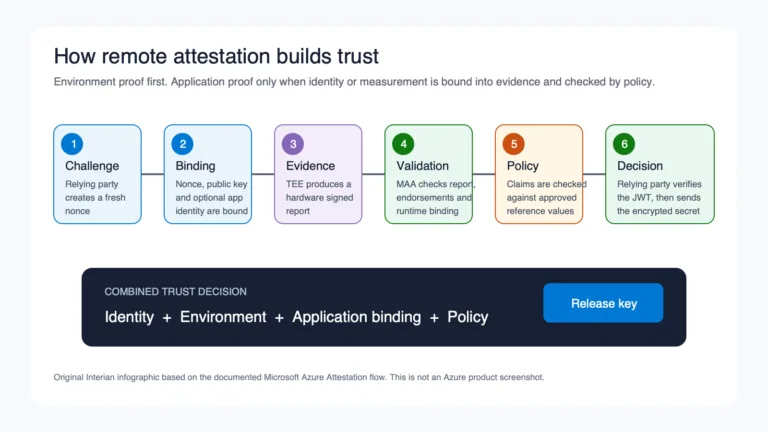
Azure Attestation provides cryptographic evidence for confidential workloads. Learn the trust flow, policy checks and relying-party decisions.
Practical Microsoft security, identity and governance insights

Practical Microsoft security, identity and governance insights
Practical guidance on Microsoft Entra, Purview, Intune and Microsoft 365 security governance, focused on real tenant configuration, operational risk and governance controls.
Identity governance, Conditional Access, PIM, passwordless, recovery, administrative boundaries and group governance.
Data protection, DSPM, DLP, Copilot, AI governance and compliance architecture.
Configuration management, security baselines, configuration drift and continuous control.
Microsoft security controls, evidence, risk management and practical compliance.
Understand policy gaps, token and session risks, and the defensive controls that reduce exposure.
What native recovery covers, where its limits remain and how to plan for operational resilience.
Move from flat tenant administration to scoped ownership and defensible governance boundaries.
Connect group ownership and lifecycle decisions to access reviews and enforceable governance.
Make configuration drift, baseline monitoring and control evidence part of ongoing tenant governance.
Turn AI policy into practical responsibilities and controls across Copilot, Purview and Entra.
Azure Attestation provides cryptographic evidence for confidential workloads. Learn the trust flow, policy checks and relying-party decisions.
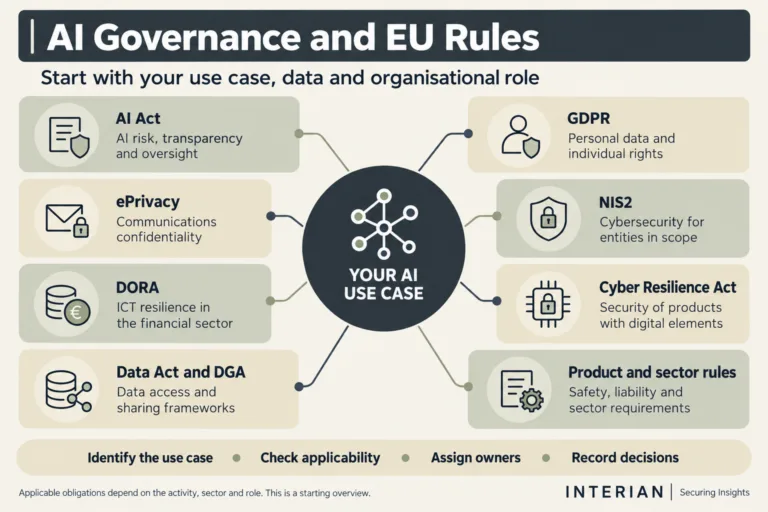
A practical starting point for AI governance: discover your tools, assign owners, assess data and autonomy, check EU rules and plan the first controls.
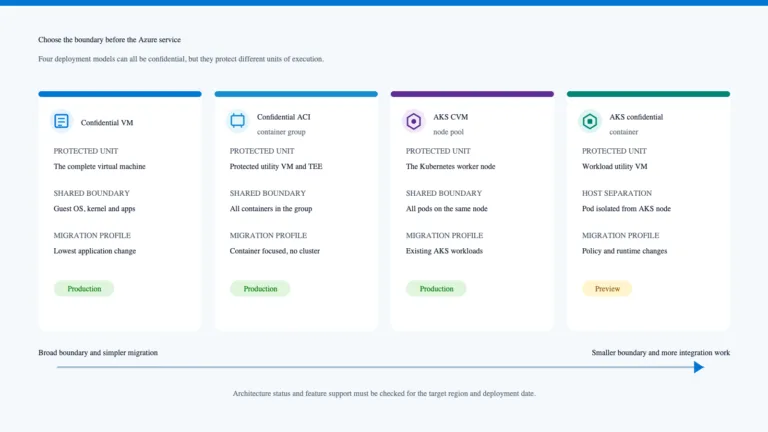
Choose the right Azure confidential computing model for VMs, ACI or AKS. Compare trust boundaries, deployment options and operational trade-offs.
TL;DRWindows 11 Point in Time Restore rolls a PC back to a recent local snapshot. Intune can deliver the configuration; the documented restore runs locally in Windows Recovery Environment.Check supported builds, available restore points and BitLocker recovery key access before…
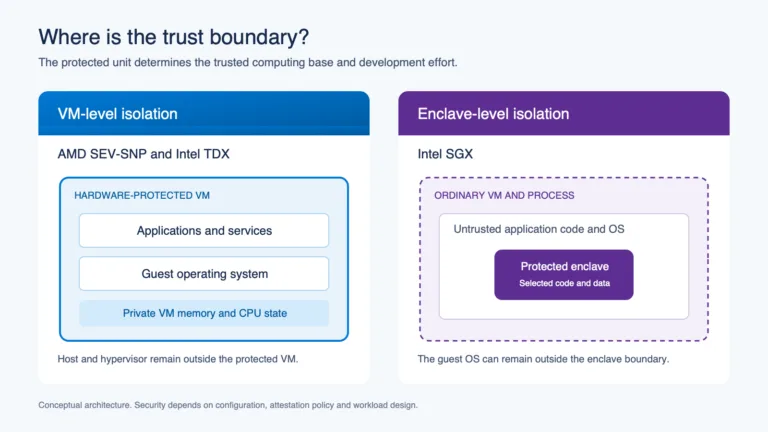
Compare AMD SEV-SNP, Intel TDX and Intel SGX: trust boundaries, attestation models, workload fit and practical security trade-offs.
TL;DRTo block personal accounts in Copilot, configure Microsoft Entra tenant restrictions and enforce them on the relevant network or device path.Intune can deliver the Windows policy, but deployment success alone does not prove coverage across every browser and app.Keep access…