AI Governance Where to Start
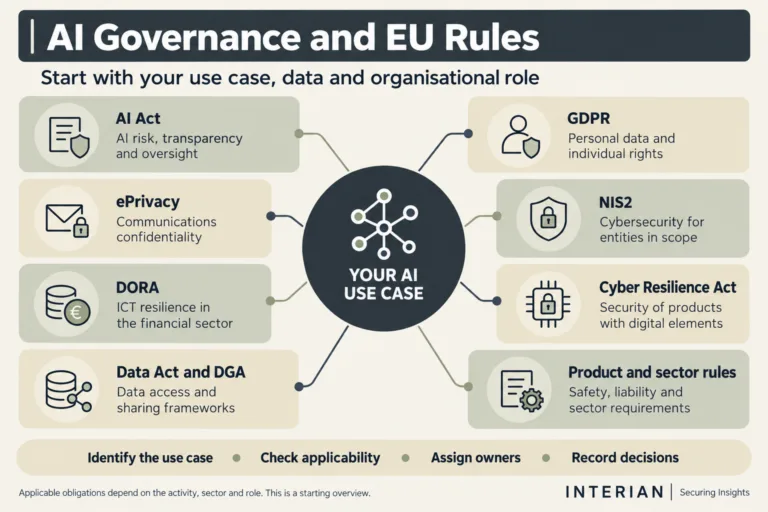
A practical starting point for AI governance: discover your tools, assign owners, assess data and autonomy, check EU rules and plan the first controls.
Practical Microsoft security, identity and governance insights

Practical Microsoft security, identity and governance insights
A practical starting point for AI governance: discover your tools, assign owners, assess data and autonomy, check EU rules and plan the first controls.

Microsoft recently shared how its Office of the CISO manages cybersecurity risk at hyperscale. While the tooling and governance structure are impressive, most organisations cannot simply copy Microsoft's operating model.
AI Governance in Microsoft 365 operating model for Copilot, Purview, Entra, Defender, ISO 42001 and EU AI Act readiness.
Entra Tenant Governance explained with practical risks, governance impact and next steps for Microsoft security, identity and cloud teams.
Microsoft is introducing Tenant Configuration Management as a native configuration governance layer for Microsoft 365. This article explores how continuous configuration monitoring, drift detection and baseline enforcement will reshape Microsoft security and compliance operating models.

Conditional Access is the backbone of Zero Trust in Microsoft Entra ID, yet real world attacks increasingly demonstrate how it can be bypassed. From device and token abuse to built in exclusions and misunderstood session controls, attackers exploit gaps that many organisations assume are protected.
Triggered by Microsoft’s upcoming change in February 2026, where session revocation will finally behave as expected during incident response, this blog analyses observed Conditional Access bypass techniques from real incidents in 2024 and 2025. More importantly, it explains why a strong security baseline is essential to compensate for what Conditional Access was never designed to solve alone.

Discover the game-changing 'Require Risk Remediation' control in Microsoft Entra Conditional Access. This preview feature simplifies risk management by handling both password and passwordless users in one policy, reducing complexity and misconfigurations. Get a step-by-step guide, real-world benefits, and pragmatic insights into its limitations for enhanced security.
Many organisations assume Microsoft Entra ID handles guest users securely by default—but it doesn't. In this post, we uncover the top 5 common mistakes in guest access management, from excessive directory visibility to perpetual access without lifecycle controls. Learn how to lock down your tenant with practical fixes, ensuring secure B2B collaboration without the risks.
A practical look at Microsoft’s Baseline Security Mode: what it does, where it helps, and how it supports essential cyber hygiene under standards like Cyber Essentials and NIS2.
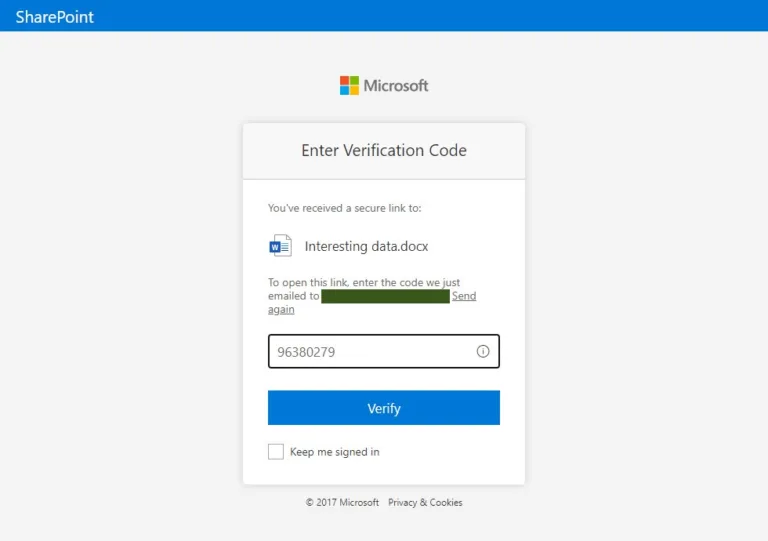
Microsoft is phasing out One-Time Passcode (OTP) authentication for SharePoint Online and OneDrive external sharing, replacing it with Entra ID B2B Collaboration, effective July 1, 2025 (MC1089315). Legacy OTP links will stop working, requiring users to re-share content to restore access for external collaborators, who must also register for mandatory MFA. Prepare now by notifying users, updating documentation, auditing shared content, and ensuring Entra ID B2B settings are configured. This shift enhances security but demands proactive planning to avoid disruptions.