Entra Tenant Governance: How It Works in Practice
Entra Tenant Governance explained with practical risks, governance impact and next steps for Microsoft security, identity and cloud teams.
Practical Microsoft security, identity and governance insights

Practical Microsoft security, identity and governance insights
Entra Tenant Governance explained with practical risks, governance impact and next steps for Microsoft security, identity and cloud teams.
Administrative Boundary Design in Microsoft Entra explained with practical risks, governance impact and next steps for Microsoft security, identity and
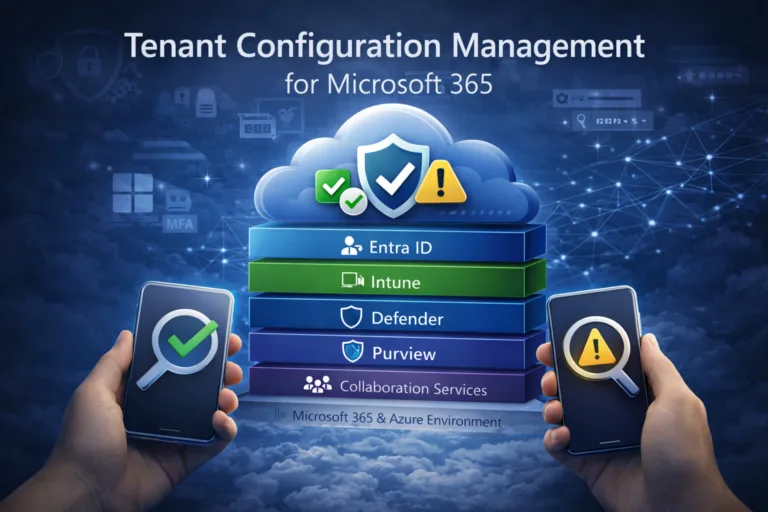
Microsoft is introducing Tenant Configuration Management as a native configuration governance layer for Microsoft 365. This article explores how continuous configuration monitoring, drift detection and baseline enforcement will reshape Microsoft security and compliance operating models.
Microsoft is automatically enabling passkeys in Entra, accelerating the shift to passwordless authentication. This technical deep dive explains configuration, device sync behaviour and best practices for deploying passkeys securely with Conditional Access.

Conditional Access is the backbone of Zero Trust in Microsoft Entra ID, yet real world attacks increasingly demonstrate how it can be bypassed. From device and token abuse to built in exclusions and misunderstood session controls, attackers exploit gaps that many organisations assume are protected.
Triggered by Microsoft’s upcoming change in February 2026, where session revocation will finally behave as expected during incident response, this blog analyses observed Conditional Access bypass techniques from real incidents in 2024 and 2025. More importantly, it explains why a strong security baseline is essential to compensate for what Conditional Access was never designed to solve alone.

Discover the game-changing 'Require Risk Remediation' control in Microsoft Entra Conditional Access. This preview feature simplifies risk management by handling both password and passwordless users in one policy, reducing complexity and misconfigurations. Get a step-by-step guide, real-world benefits, and pragmatic insights into its limitations for enhanced security.